AI governance, compliance and security — the practical guide
Field notes from shipping governance infrastructure for legal, fintech and healthcare teams. No fluff, no vendor speak.
Sensitive data discovery tools for AI: detecting PII before it reaches LLMs
Classic sensitive data discovery tools scan databases and file shares. They were never built to stop PII inside a prompt on its way to ChatGPT, Claude or Gemini. Here's how the two approaches compare — and what to look for.
Read post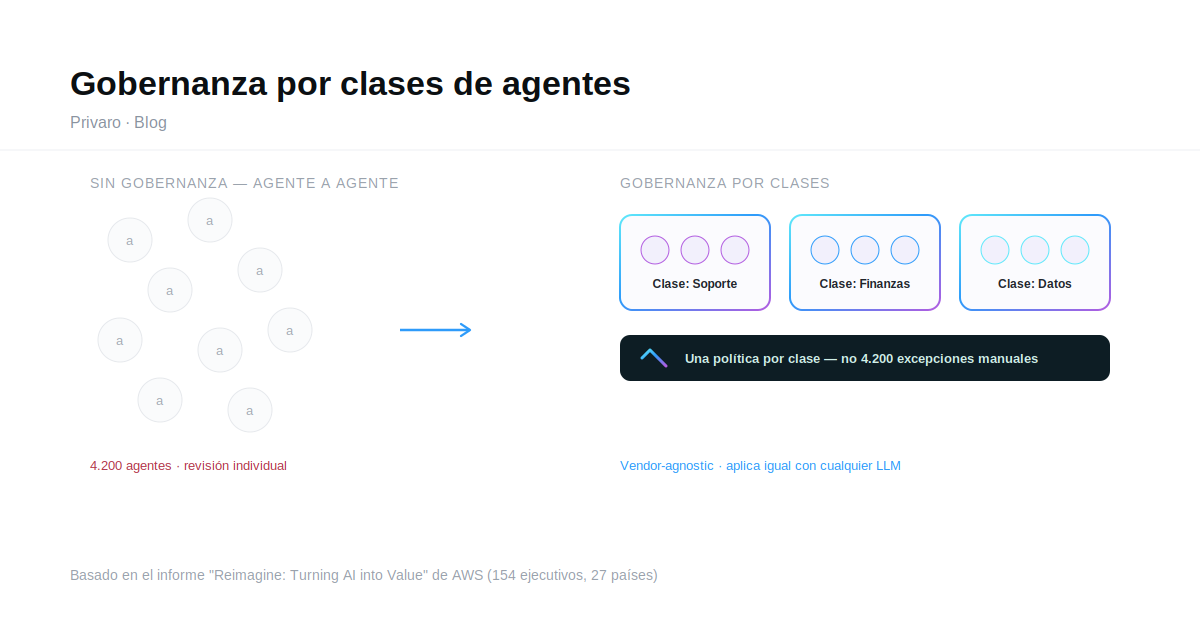
When 4,200 AI agents make decisions at once, governing them one by one stops working
AWS interviewed 154 executives across 27 countries for its Reimagine report. One finding: governing AI agents individually does not scale — governance needs to work by agent class.
Read postGoverning AI Agents: Why Monitoring Is No Longer Enough
Agent inventories and performance dashboards provide visibility, but not data control. Learn how to govern sensitive data at runtime across every AI agent interaction.
Read postCase Study: Governing Robin AI, Octupus's ERP Copilot for Odoo
How Octupus Technologies put Privaro between Robin AI and the model so ERP agents can read customer, invoice and margin data without exposing it to the LLM.
Read postPII in RAG Pipelines: Protect at Ingest and at Retrieval
A vector store is a copy of your documents. How Privaro Ingest and Retrieval Guard keep personal data out of embeddings and out of the model's context window.
Read postAI Governance Tools in 2026: How to Choose One
A buyer's guide to AI governance tools: the four categories on the market, the eight controls that matter in regulated industries, and the questions to ask vendors.
Read postPII in LLM Outputs: Why Input Filtering Is Not Enough
Models can emit personal data you never sent them. How output scanning works, why SSE streaming is audit-only, and how to design a pipeline that catches leaks.
Read postAI Compliance Software: What Auditors Actually Ask For
The evidence auditors request for AI systems under GDPR and the EU AI Act — and how to produce it automatically with AI compliance software.
Read postAI Governance Platform: A 2026 Buyer's Guide
What an AI governance platform must do in 2026: PII detection, policy enforcement, tokenization, output scanning and audit evidence. Evaluation criteria and pitfalls.
Read postGDPR Checklist for LLM Applications (2026)
A practical GDPR checklist for teams shipping LLM-powered apps: lawful basis, data minimization, DPIA, retention and third-country transfers.
Read postEU AI Act Compliance for SaaS: What Ships in 2026
How the EU AI Act applies to SaaS products using LLMs — risk tiers, GPAI obligations, transparency requirements and a practical roadmap.
Read postHow to Mask PII Before Sending Prompts to OpenAI
A developer guide to detecting and masking PII in prompts before calling OpenAI, Anthropic or Gemini — with code samples and reversible tokenization.
Read postOpenAI vs Anthropic: Data Privacy Compared for Enterprise
A side-by-side comparison of OpenAI and Anthropic data privacy: retention, training on customer data, EU residency, DPAs and audit posture.
Read post